RSS Feeds
YouTuber arrested after popular Indian finance influencer's suicide
How a Legal Backlash Against Big Tech Is Forcing Big Changes
Teacher injured in Oregon shooting shares emotional survival story
Mark Zuckerberg threatened to leave California over wealth tax
Поколение Z военного времени. Почему российская молодежь не протестует? | При участии Екатерины Шульман
PC Sharon Beshenivsky killer jailed over underworld guns operation
John Anderson, country artist known for ‘Seminole Wind,’ dies at 71
Tell us: have you been affected by the PHP code flaw?
We’d like to hear from small businesses that have been affected by the PHP code flaw. Did you have to take you website offline? Did you manage to patch the fault?
Websites around the world have been hit by millions of attempts to exploit a recently discovered vulnerability in their code, cybersecurity companies have said, as the US National Security Agency warned the flaw could allow attackers to take control of web servers, steal data and disrupt services.
The problem in the PHP programming language, which underpins about 70% of the world’s websites, emerged on Wednesday causing governments and companies to pull their websites off the internet before they could be attacked and so they could patch the fault.
Continue reading...The Brief, Messy Political Career of Paolo Zampolli, a Trump Ally
‘Jane Austen is for everyone’: novelist Diana Reid on adapting Sense and Sensibility – and surprising Brits with her accent
The Australian author of Love and Virtue says her nationality didn’t give her pause when she wrote the script, but Ang Lee’s ‘perfect’ 1995 film did
The summer Diana Reid spent writing her film adaptation of Sense and Sensibility, she found herself having some oddly formal conversations down at the pub. The Australian author used only about 25 lines from Jane Austen’s first published novel for her screenplay, inventing most of the dialogue herself. To be able to mimic that very distinctive voice, Reid had to dive headfirst into studying Austen’s rhythm and sentence structure.
“I got so immersed in the language it infected my own speech. I would be describing someone I just met, and I’d be like, ‘Oh, he was most amiable!’” Reid says, laughing. “It was a kind of insanity.”
Continue reading...Surfing faces a cultural reckoning as women’s voices grow louder over sexual abuse allegations | Lucy Small
A culture of silence has buried the stories of women who allege sexual assault in surf industry settings
When news broke last week that a surfer had been provisionally suspended from international competition, after what the International Surfing Association (ISA) described as “recent reports of serious allegations of abuse within the surfing community,” the response online was unprecedented in the world of surfing.
While investigations into those allegations are ongoing, the story prompted a deluge of comments detailing other alleged experiences of sexual misconduct and assault in surf industry settings, ranging from corporate brand houses in Hawaii to organised surf trips. While horrifying, for women who have existed in this subculture across the decades, those broader stories are sadly no surprise.
Lucy Small is a professional surfer, journalist and film-maker from Sydney, with a special interest in women’s sport
Continue reading...Как я устраивался SEO‑руководителем в сервис ИИ презентаций Slidy, а получил оффер на специалиста
У Slidy есть отличный слоган — «Самая быстрая нейросеть для презентаций». Как выяснилось, в компании довольно быстро могут меняться и предлагаемые должности. Причем кандидат узнает об этом уже из оффера.
Расскажу, как я проходил собеседования на руководителя отдела SEO‑контента, выполнял тестовое задание, общался с директором и действующим руководителем, а в итоге получил предложение на совсем другую позицию.
Читать далееA financially comfortable friend has set up a GoFundMe for vet bills. Is this socially acceptable? | Leading questions
Your friends may have had good intentions when making this request, writes advice columnist Eleanor Gordon-Smith. But that needn’t dictate how you feel about it
Read more Leading questions
A friend, who I believe is financially comfortable, set up a GoFundMe page to pay for vet bills for their sick dog while on holiday overseas.
The family appears to be financially comfortable; both adults have good jobs, own two cars, have all the latest gadgets like expensive bikes and sporting equipment, take an annual holiday overseas and domestic holidays throughout the year, and live in a big house in a well-to-do area.
Continue reading...«Ксеноморфный софт, который вырос у меня дома». Колонка Сергея Рыжикова
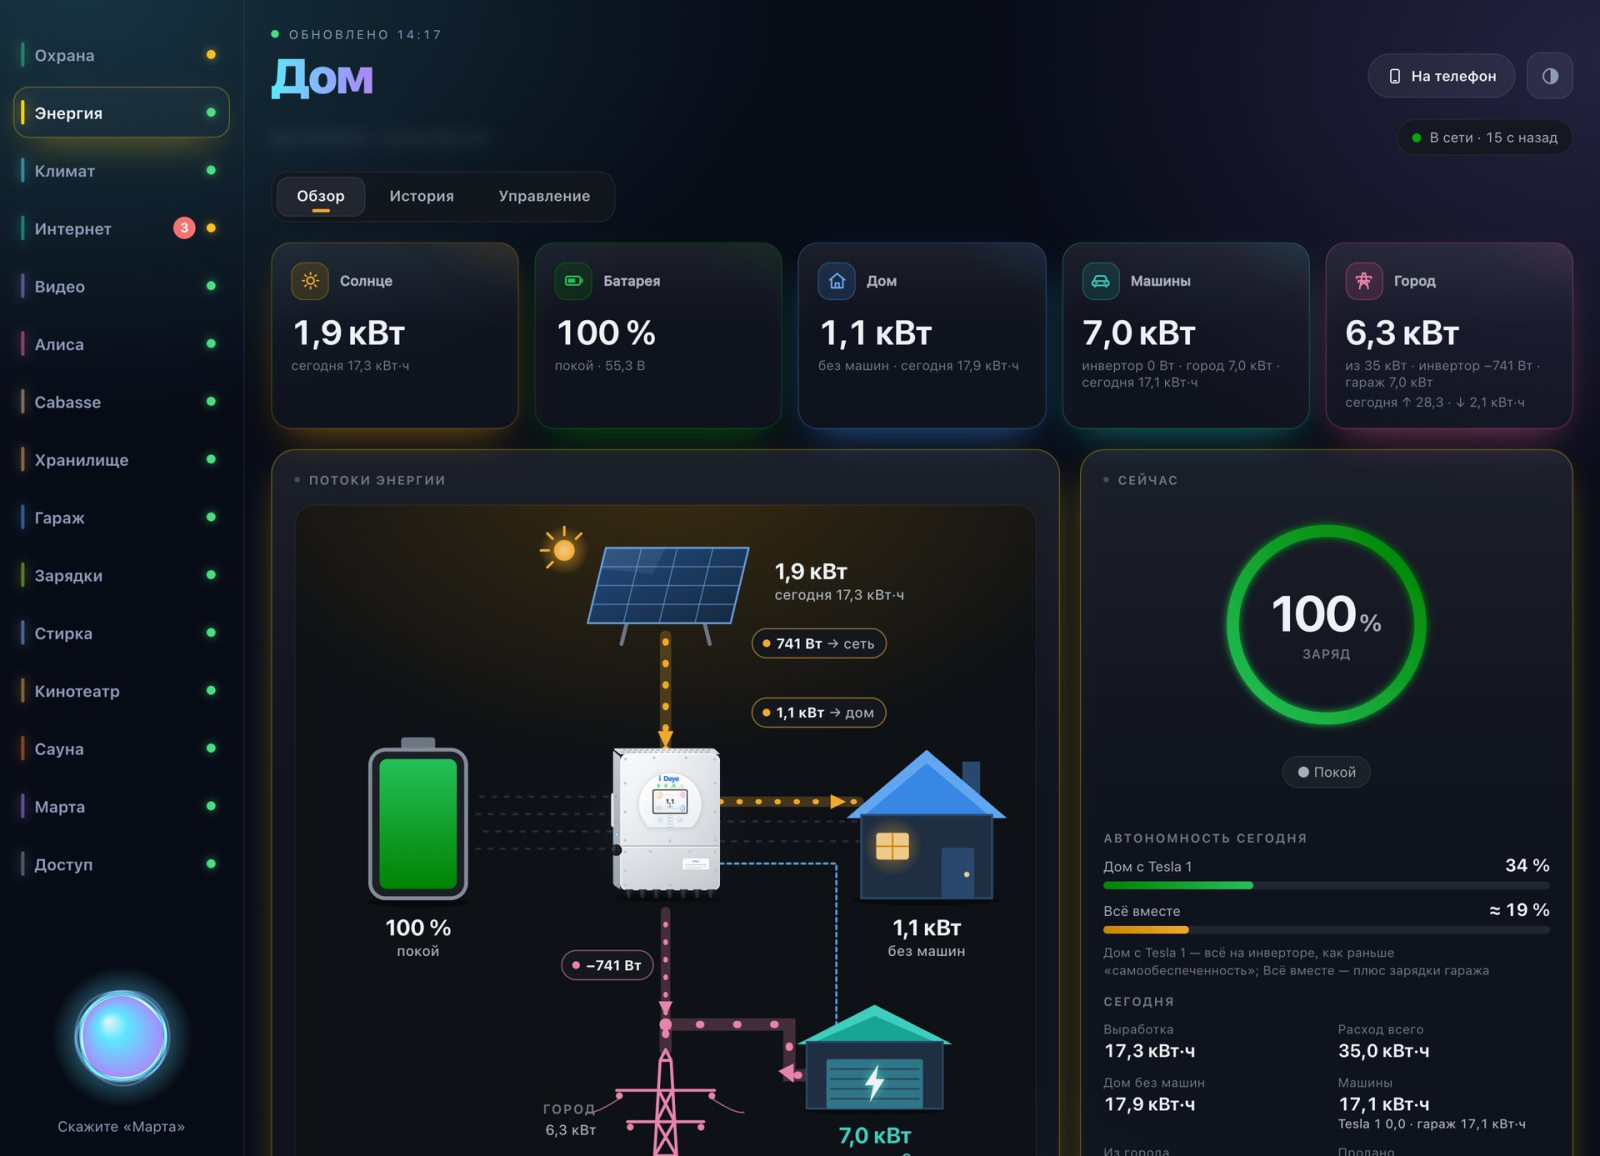
Представляем вам колонку, написанную Сооснователем компании Битрикс24 Сергеем Рыжиковым.
Почти десять лет назад я рассказывал, как мой дом научился жить на солнечной энергии. Сегодняшняя история тоже начинается с солнечной электростанции. Но этот рассказ будет про другое: про то, как у меня дома выросла программа. Почти сама.
Я давно думаю об одной вещи. Сколько я себя помню в софте, программы всегда поставлялись готовыми. Их проектировали заранее, отливали в одну форму и раздавали всем одинаковыми. Можно было подкрутить настройки, включить или выключить какие-то функции, и на этом все. Если твоего устройства нет в списке поддерживаемых, извини. Подстраиваться всегда приходилось человеку. Мне давно казалось, что должно быть наоборот, но как это сделать, было непонятно — до недавнего времени.
Читать далееTeacher in Oregon shooting said she pretended to be dead to survive
U.K. interests in the Arctic are vulnerable to Russia, lawmakers warn
Выживаем при PHP2Shell (CVE-2026-109618 / CVE-2026-109619) на легаси‑стеке: Varnish + Docker + Apache mod_php (PHP 5.6)
21 октября 2026 года мир PHP вздрогнул от анонса двух критических RCE-уязвимостей (CVSS 9.2), получивших общее имя PHP2Shell (CVE-2026-109618 и CVE-2026-109619). Опасность этих брешей в том, что они срабатывают на уровне ядра интерпретатора еще до того, как управление дойдет до первой строчки вашего index.php. Достаточно, чтобы сервер просто принимал HTTP-запросы.
Разработчики PHP оперативно выпустили патчи для поддерживаемых веток (8.2.35, 8.3.36, 8.4.27, 8.5.12) и заявили: «Единственный 100% способ защиты - обновление, а сценарий наивысшего риска - это Apache с mod_php».
Звучит отлично, если у вас свежий проект. А что делать, если в продакшене крутится суровый высоконагруженный энтерпрайз-легаси на PHP 5.6 в связке с Apache 2.4 (mpm_prefork + mod_php), переписать который за ночь невозможно, а официальных патчей для ветки 5.6 не выйдет никогда?
Под катом - практический разбор того, как устроены обе уязвимости, почему именно mod_php оказался под главным ударом и как я выстроил эшелонированную оборону на уровне Varnish → Apache → PHP → Docker cgroups, не сломав легаси-монолит и проверив каждый рубеж боем (с разбором подводных камней HTTP keep-alive).
Celebrity shark guided out of South Korea canal refuses to swim out to sea
Teacher in Oregon shooting said she pretended to be dead to survive
Single-tenant Titus: VM-level isolation on a multi-tenant container platform
Samartha Chandrashekar & Nick Parker
You click play on a Friday night, and in the second that follows, dozens of services answer in milliseconds. Most of them run on Titus, our internal container platform. Titus is, in essence, a Kubernetes-based container hosting platform: we keep both the control plane and the data plane (the container hosts that actually run containers) patched and up to date, so application teams get a consistent and reliable container experience. They hand us a container, and we run it, with no host, cluster, or kernel to own. Titus launches millions of containers every week across tens of thousands of EC2 instances in multiple AWS regions. It is multi-tenant by default: many containers from many teams share each host. That density is what makes container compute efficient, and it is why Titus has been the default home for so much of Netflix’s compute for years.
For most workloads, sharing a host works well. For a few, it does not, and those few include some of the most demanding real-time systems we run. This post is about them, and about single-tenant Titus, a mode that gives a task its own virtual machine while keeping everything else about Titus the same: the API, the deployment path, and the managed experience where the Compute/Platform team, not the application team, owns the host.
We will walk through why shared-kernel isolation runs out of road for certain workloads, how we measure isolation rather than asserting it, the options we weighed (microVMs, gVisor, EC2, and more shared-kernel tuning) and why a dedicated VM inside Titus won, how the mode is built on the Titus federation layer and autoscaling, and what we have seen along three axes: isolation, fleet efficiency, and the operational cost of keeping the fleet patched.
The cost of good neighbors
Multi-tenancy is a tradeoff. Packing many containers onto a large bare-metal instance keeps utilization high, but it also means those containers share a single Linux kernel and the underlying hardware. Titus isolates them with the tools the kernel provides: cgroups cap CPU, memory, and disk; namespaces give each container its own view of the system; seccomp and AppArmor restrict the system calls a container can make; the Completely Fair Scheduler divides CPU time; the iocost controller meters disk IO; and traffic shaping meters each container’s slice of the network. Each container also gets its own identity, IAM role, and security groups, so tenants are isolated for security and resource management.
These mechanisms provide isolation for what the kernel can partition. They cannot fully partition what is shared in hardware. A group of cores shares a last-level cache and a path to memory, so a container that suddenly pulls a lot of data from RAM evicts a neighbor’s cache lines and slows it down, even when both stay inside their CPU limits. There is no cgroup for memory bandwidth or cache residency, as there is for CPU shares. The interference is real, it is hardware, and it does not show up as either container exceeding its quota.

We have written about this before. Predictive CPU isolation of containers at Netflix moved some placement decisions out of the kernel and into a service that forecasts each container’s CPU demand and re-pins containers to cores to reduce cache interference, formulated as a combinatorial optimization solved every minute. Noisy Neighbor Detection with eBPF instruments the kernel scheduler to surface per-container run-queue latency, so we can see a victim being starved in close to real time. And Mount Mayhem traced container-startup slowness to a global kernel lock amplified by modern CPU cache topology. Each of these raised the floor for everyone on the platform, and we are continuing that work.
A decade of shared-kernel isolation, at Netflix and across the industry, has not made co-tenancy invisible, because a noisy neighbor is not one problem but a family of them. Almost every physical resource a host shares is its own axis of interference, and a cgroup can fence very few of them:
- CPU performance indeterminacy. Co-located threads contend for the run queue, so scheduling latency rises even while a container remains within its CPU quota. Separately, a neighbor with a large working set evicts a tenant’s last-level cache lines and saturates memory bandwidth, neither of which a CPU share can partition.
- Network bandwidth and packets per second. Per-container shaping competes for link bandwidth, and receives processing runs in softirq context, charging one container’s packet work to whatever CPU a neighbor is running on. A flood of small packets exhausts a core’s softirq budget long before any bandwidth cap is reached.
- Storage bandwidth and IOPS. A neighbor saturating a device’s queue serializes everyone’s I/O, and on cloud block storage, the per-volume and per-instance throughput ceilings are a shared budget in their own right.
- Long tail. Page-cache reclaim, NUMA and cross-socket interconnect traffic, TLB-shootdown interrupts, PCIe and GPU contention, package-level power and thermal throttling, and contention on kernel global locks (the class of problem behind Mount Mayhem) each degrade neighbors in their own way.
What unites them is that they are physical, shared, and below the level a quota can reach. A platform can cap how much CPU time or memory a container is granted; it cannot hand each tenant its own slice of the memory bus, its own softirq budget, or its own portion of the last-level cache.
Of these, the network dimension has bitten hardest in our experience. Per-container bandwidth shaping uses a hierarchical token bucket (HTB) queueing discipline that serializes traffic with a global lock to account for each container’s bytes and packets. Under a flood of small packets from a single container, contention for that lock can burn kernel CPU and starve co-located containers of the time they need to process their own traffic, resulting in TCP retransmits and tail-latency spikes on services that did nothing wrong. The mechanism meant to prevent noisy neighbors becomes one.
The workloads most exposed to this are stateful, high-throughput streaming jobs: real-time data pipelines and stream processors that continuously move large volumes of data and maintain in-memory state. When one of these is perturbed, recovery is not cheap. A stream processor that falls behind or loses its place may have to restore from a checkpoint and pause processing for many minutes to catch up. For these jobs, intermittent interference from a neighbor is not a small slowdown that averages out; it is a stop-the-world event that pages an on-call engineer. The same teams report, accurately, that they never saw this on a plain EC2 instance.
Why we kept coming back to the VM
Full VM isolation, where a workload gets its own host and kernel, is the standard our customers are already happy with. The question was not whether VM isolation works; it was how to offer it without giving up what makes Titus worth using. We weighed four paths.
- Keep improving shared-kernel isolation. This helps every workload on the platform, needs no opt-in, and we are still investing in it (more on the roadmap below). Its limitation is structural. Each round of tuning narrows the gap without closing it, because the underlying hardware remains shared. Cache, memory bandwidth, and the kernel’s own shaping and scheduling locks are not things a container boundary can fully contain. Shared-kernel isolation is the right default and the wrong promise for a workload that cannot tolerate a bad minute.
- microVMs (Firecracker, Kata Containers). Lightweight VMs boot in about 150 milliseconds by emulating far less hardware than traditional VMs, which is why they power serverless platforms. They were the most appealing alternative on paper, and we carefully reviewed them. Three things made the cost hard to justify. First, the hardware virtualization they rely on is available only on bare-metal instances or through nested virtualization, and nested virtualization was not ready on the instance types we run at Netflix at the time, so adopting microVMs broadly would have constrained us to a narrow slice of the fleet. Second, there is no managed microVM service we could build on, which means we would have to run and maintain a virtualization layer ourselves: patching the hypervisor, live-migrating guests, and qualifying emulated devices. That is exactly the kind of operational surface we prefer not to own when we can avoid it. Third, even setting those aside, microVMs add virtualization overhead on CPU- and IO-bound work and do not support GPUs. Excellent isolation, but at a price in flexibility and operational load we were not willing to pay.
- gVisor. A user-space kernel that intercepts system calls provides sandbox-grade isolation without a hypervisor, thereby avoiding the bare-metal constraint. The catch is performance and dependency. Intercepting syscalls in user space adds overhead on IO-heavy paths, which are precisely the workloads we most need to protect, and the open-source project lags behind its internal counterpart in fixes and is effectively maintained by a single vendor. The isolation we would gain came with a throughput tax on the exact jobs we were trying to help.
- Move the workload to EC2. It is possible to run containers directly on EC2 instances. The problem is that the application team takes back the operational load that Titus exists to carry: choosing instance types, patching hosts, and sizing and scaling the fleet. For a team that came to Titus precisely to avoid those things, this is a regression in the experience, and the move between Titus and EC2 has historically been a one-way door that teams are reluctant to cross.

There is also a question of what kind of isolation we actually need. microVMs and gVisor are built for security isolation between mutually distrusting tenants, the case where one tenant might actively try to attack or escape into another. Among Netflix teams, that threat model is more than the situation warrants. What these workloads need is resource and performance isolation: a guarantee that a neighbor cannot steal their CPU, cache, memory bandwidth, or network, not protection from a hostile co-tenant. A dedicated EC2 VM delivers exactly that, with hardware we do not have to emulate and a kernel we do not have to sandbox. We pay for the isolation we need rather than for a stronger security boundary.
microVMs and gVisor asked for a large, bespoke investment with real risk in order to approximate something we could get directly: a VM. Using EC2 to run containers provides the VM, but takes away the managed experience. So we took the direct route and brought single-tenant VM isolation into Titus itself, under the existing API and the existing shared-responsibility model.
How single-tenant Titus works
The idea is simple to state: a single-tenant task runs on its own EC2 instance, sized to fit it, with nothing else scheduled alongside. That instance is still a Titus container host that the Compute/Platform team owns and patches. The team running the workload sees the same Titus API and the same deployment path. Nothing about how they package or ship the job changes.

Most of the work happens in the federation layer, the part of Titus that decides where a job runs (which cell, which capacity) before it is scheduled onto a node.

When a job is eligible for single tenancy, three things happen.
- Federation decides eligibility and the envelope. Eligibility is governed by an allowlist maintained by the Compute/Platform team; a team opts in by targeting a single-tenant workload group rather than flipping a flag in the public API. For an eligible task, federation tags it as single-tenant and records the set of instance families it may run on, ensuring consistent performance across the workload. Consolidating this decision in federation follows the same principle we use for routing in general: placement intelligence belongs in one place, above the individual cells, where it can account for capacity and availability across the region.
- Autoscaling provisions a dedicated node. Given a pending single-tenant task, our autoscaling implementation launches the smallest instance that satisfies the task’s requested CPU, memory, and GPU from the allowed families for the task just in time. Taking the tightest fit keeps the unused remainder of each dedicated node small. The next section covers this in detail.
- The scheduler enforces one task per node. Single-tenant pods are configured with pod anti-affinity to prevent colocation with other pods, along with a priority class that exempts the task from preemption. Single-tenant nodes are also tainted to prevent unrelated workloads from being placed there, with only single-tenant workloads tolerating this taint. We also disable defragmentation/repacking for these nodes, so a single-tenant task is never relocated to repack the fleet. Together, these mean a single-tenant task has its host to itself for its entire life, undisturbed by a neighbor or by the platform’s own bin-packing.
Two design choices are worth dwelling on. First, single tenancy is allowlisted on purpose. If it were a free checkbox in the API, most teams would tick it, because who wouldn’t want a quieter host? And the efficiency that multi-tenancy exists to provide would erode across the fleet. Keeping the Compute/Platform team in control lets us direct dedicated isolation to workloads that need it and steer the rest toward shared capacity, while keeping the public API surface small as we learn. Second, we do not silently resize anyone’s job to fill its node. The job keeps the resources it requested; we recommend sizing it close to a node shape so the dedicated instance is well utilized, while keeping the workload portable and running identically whether in single-tenant mode or not, regardless of the host’s dimensions. Moving in and out of the mode is a configuration change, not a rewrite.
A few perpetrators, a lot of collateral damage
Noisy-neighbor pain is not spread evenly. In practice, a small number of workloads cause most of the disruption: a job that floods the host with small packets, churns the page cache, or saturates memory bandwidth degrades the performance of every other container unlucky enough to share its host. Some of these are also among the workloads most affected by contention, because a job can be both a source of interference and sensitive to it. The shape of the problem is a few perpetrators and many victims.
That shape is what makes single tenancy a precise lever rather than a blunt one. We do not need to give every workload its own machine. We need to pull the handful of perpetrators and the most disruption-sensitive victims onto dedicated nodes. Doing so protects their former neighbors directly and removes the reason the platform was spreading sensitive workloads apart with anti-affinity placement in the first place. The hosts left behind are quieter, and because they no longer have to be kept partly empty to honor spread rules, they pack more densely.

On the left is the fleet before: perpetrators sit on shared hosts, the workloads next to them suffer, and anti-affinity rules leave gaps that cannot be filled. On the right is the same fleet after: each perpetrator has its own right-sized node where it can be as noisy as it likes, with no one to disturb; the remaining hosts run full of undisturbed workloads; and the capacity that used to be stranded comes back. A few dedicated nodes buy isolation for the perpetrators and a calmer, denser fleet for everyone else.
Provisioning many small nodes
Single tenancy trades fewer large, shared instances for more small, dedicated ones, and that shift has consequences across the stack.
The first is the control-plane load. More nodes mean more for the Titus control plane to track and more VM launches against the EC2 control plane, the latter mattering most during a regional failover, when we scale up the fastest and can least afford a throttle. Titus is already a federated system: each region is divided into independent cells, which limit how large any single control plane can get, and let us add capacity by adding cells rather than growing a single stack without limit. We migrate workloads in stages rather than all at once, and we exercise the launch-rate path under controlled load on a schedule rather than discovering its limits during an incident.
The second consequence is capacity management, where the design changed the most. With one task per node, the fleet now spans many instance shapes whose demand shifts continuously as jobs come and go. Pre-staging static pools of every shape would be slow to manage and wasteful, so we instead provision single-tenant nodes on demand. It handles provisioning end-to-end, and several of its features line up with exactly what single tenancy needs:
- Just-in-time, right-sized provisioning. Single-tenant jobs are configured with a list of supported instance families based on their performance requirements. At launch, they are mapped to the best-fit node size by comparing requested resources against the selected instance families. New nodes of that instance type are brought up by the autoscaler to meet the pending demand. Single-tenant pods are configured with anti-affinity to all other pods, so the scheduler naturally lands one pod per autoscaled node. Newly vacated nodes may be reused by any pending deploys before they’re automatically torn down. The node pools themselves are shared across single-tenant workloads and describe a catalog of available instance families and sizes.
- Single tenant node pools. Single tenant may run in separate clusters or be shared with multitenant clusters. The pools are configured with a list of supported instance-type permutations and are pinned to a Titus container host AMI. This is where the managed experience lives: the host image and its configuration are ours, declared once and applied to every node created.
- Consolidation management. In multi-tenant environments, we default to a repack/defrag behavior that periodically relocates workloads. This doesn’t apply in single tenant, where nodes are explicitly each running at most one workload. We therefore reclaim only nodes vacated by workloads that have scaled in or terminated. Node termination is performed in two stages, allowing nodes to be reused for pending workloads before they are fully terminated.
- Drift-based patching. When we publish a new container host AMI, we support a “mutable” deploy to existing nodes without affecting any hosted containers, and an “immutable” deploy that updates the target AMI for newly created nodes. This means that many node upgrades don’t require disrupting workloads, but we reserve the right to roll the fleet with our users if needed.
The launch-latency tax, and why warm pools are harder here
Provisioning on demand does not make a node appear instantly, and launch latency is the tradeoff single tenancy asks us to manage most carefully. Bringing a single-tenant task to the point where it can serve traffic has two parts: standing the node up (booting a fresh EC2 instance, then pulling and extracting the container image, which is the largest part of host setup for most jobs) and the application’s own startup (a JVM loading and JIT-compiling its classes, a cache filling, and so on). A fresh instance takes tens of seconds before the image pull even begins.
In multi-tenant Titus, most of this is hidden. A new task usually lands on a Titus container host that is already running and already has the image layers cached, so starting it takes only a few seconds rather than minutes; the host boot was paid for once, long ago, and amortized across every task that has run there since. Single tenancy gives up that hiding place. Every single-tenant task waits for its own machine to boot and pull its image.
The usual remedy is a warm pool: keep some instances booted and idle so a pending task lands on one immediately. This works well for the multi-tenant fleet precisely because that fleet is close to homogeneous. A handful of large shapes cover almost everything, since any task can be packed onto a big shared host. A small amount of warm capacity in a few shapes gives a high hit rate, and its cost is spread across the many tasks that will use it.
Single tenancy inverts those economics, and this is the part worth being explicit about.

Because every task gets a right-sized node, the fleet spans many instance shapes (several families across many sizes), and a warm instance only helps a pending task whose shape matches it. A warm r7i.2xlarge does nothing for a task that needs an m7a.8xlarge. To achieve a good hit rate, we would need to hold idle capacity in every family-and-size bucket, and idle capacity in a bucket with no task to fill is pure cost. The very property that makes single tenancy efficient at steady state, tight best-fit sizing, works against warm-pool reuse: more distinct shapes mean more buckets and a lower hit rate per dollar of standing capacity. And the pressure peaks exactly when it is least welcome. During a regional failover or a live event, when many tasks need fresh nodes at once, a thin warm pool spread across many shapes drains immediately, and the rest of the demand pays the full cold-boot cost.
So we treat warm capacity as a small, targeted lever rather than a default. We keep a little pre-warmed capacity for the most latency-sensitive single-tenant starts, and we deliberately narrow the menu of shapes to a curated set of sizes rather than the full continuum, so warm capacity concentrates into fewer buckets and trades a little best-fit efficiency for a better hit rate. Everything else provisions just-in-time and accepts the boot.
The more durable wins are in cutting the launch cost itself rather than pre-paying for it, and they help both single- and multi-tenant nodes, which is the better place to spend the effort:
- Faster image distribution. The image pull dominates the host setup, so newer OCI image formats and lazy-pulling snapshotters such as stargz and SOCI, which fetch only the bytes a container actually reads at startup rather than the whole image up front, reduce the largest component of the gap.
- Checkpoint and restore. For processes that are slow to initialize, snapshotting a warmed-up application with a tool like CRIU and restoring it, rather than cold-starting it, removes most of the second half of launch latency.
- Instance type selection. In multitenant configurations, we have historically used metal instances, which offer slightly better performance but come with a slower startup time. In a single-tenant configuration, node startup latency is more important, so we have moved away from these instances.
- Scheduling optimization. Through regular stress testing of fleet scaling, we found a scheduling bottleneck caused by Kubernetes preemption logic, leading to nodes being scaled up quickly but then left idle while waiting for workloads to be scheduled on them. This was ultimately unnecessary, as our single-tenant pools do not run preemptible workloads. Disabling preemption greatly improved scheduling performance when under strain.
None of this makes the tradeoff disappear, and it is worth stating plainly: a single-tenant node is slower to stand up than a slot on an already-warm shared host, and hiding that with warm pools costs more per node here than it does on the multi-tenant fleet, because the warm pool cannot be as homogeneous. But for the long-running services that single tenancy targets, paying that cost once at launch in exchange for a quiet life afterward is a trade these teams are glad to make.
Measuring the difference
Isolation claims are easy to assert and hard to trust, so we measure them with a repeatable benchmark and a single score.
The method is a differential one. We run a reference container, a healthy and representative application, and record its throughput and tail latency while it runs alone. Then we run it again next to a havoc container engineered to be a bad neighbor: a UDP flood through XDP to stress the network-shaping path, pointer-chasing and STREAM to pollute the last-level cache and saturate memory bandwidth, fsync storms against the disk, stress-ng to abuse the scheduler, and GPU-burn to monopolize an accelerator. We only trust a run once the host has reached a steady state, which we confirm with the kernel’s Pressure Stall Information: we wait until cpu_some or mem_some shows that tasks are actually stalling on a contended resource, not merely that the resource is busy. Each scenario is run many times with fixed seeds, and we report the median with a bootstrapped confidence interval, because noisy-neighbor distributions are heavy-tailed and a simple average can mask the spikes that matter.
From the reference container’s numbers, we derive a simple measure of how well isolation held. Throughput efficiency is the fraction of operations per second the app retains under attack; latency efficiency is the ratio of its undisturbed P99 to its P99 under pressure. A neighbor that doubles the reference app’s P99 drops the latency efficiency. As an illustration, a reference app whose P99 latency goes down next to a havoc container achieves a certain latency efficiency, and one whose throughput falls from a to b operations per second achieves a certain throughput efficiency. The composite score is a weighted blend of the two, with a latency-sensitive preset that gives greater weight to tail latency for interactive and streaming-path services. A perfectly isolated system scores 100%, and a single hard failure invalidates the run regardless of the average.
Noisy-neighbor isolation
cgroups container isolation isn’t perfect, and applications may experience worse performance due to sharing a machine with a determined neighbor. This could extend to disk and/or network IO where the same volumes or interfaces may be shared across workloads. For a distributed workload, this can lead to measurable inconsistencies in performance depending on where the replicas are placed. For more sensitive workloads, this variance can mean the difference between stability and getting paged.
The single-tenant option makes it possible to better isolate workloads that cause problems for their neighbors and/or are more sensitive to such problems. This can be used as a stopgap until the specific regression problem is resolved and consistency is restored, or kept permanent for load patterns that aren’t worth supporting in a shared environment.
Efficiency
The second effect is fleet efficiency, and it is the one people expect to go the wrong way. Dedicating a node to a single task consumes that node’s slack, so the naive expectation is that utilization falls. In aggregate, it can move the other way, for a reason related to how we dealt with poor isolation before single tenancy existed.
To protect sensitive workloads on shared hosts, the platform used anti-affinity placement, scattering them across the fleet to reduce colocation of the same workload on the same nodes. Spreading fights bin-packing: it strains capacity, because a host kept partly empty to honor an anti-affinity rule cannot be filled by a workload that would otherwise have fit there. When isolation-sensitive workloads move to dedicated nodes, the need for spreading and fragmentation goes away, and the remaining multi-tenant fleet can pack more densely.
Another source of fragmentation is services that are sensitive to disruption. These are typically stateful services where recovery is expensive. As these services become more common in a given population, they can lead to nodes being held up by pods with strict disruption requirements. This can lead to an inability to defrag and recompact the pool during off-peak times. The symptoms and resulting drop in fleet efficiency caused by disruption-sensitive workloads mirror what’s observed for workloads with anti-affinity rules.
Depending on the magnitude of the anti-affinity and/or disruption budget problem, moving such workloads to single-tenant pools can result in equivalent or even improved placement when all costs have been accounted for. It also becomes easier to quantify the cost to end-users. Rather than trying to attribute fleet-wide fragmentation to individual workloads, we can directly quantify waste as single-tenant node overhead.
The theory and the practice diverge here, and it was the practice that decided it. In principle, the efficiency ceiling is higher for multi-tenant bin-packing: pack enough tasks together, and a host fills almost completely. We do not reach that ceiling. AWS offers a discrete set of instance sizes, so a large shared host rarely matches the exact sum of the requests we place on it, and the gap between a host’s capacity and what we can actually pack onto it is a bin-packing hole we cannot fill. At the granularity of large instances, those holes are sizable. Right-sizing an instance to a single workload, picking the closest fit from many shapes instead of draping many workloads over one big host, captured more of the available efficiency in our experience than the higher theoretical ceiling ever delivered. The clean theory favored multi-tenancy; our measured fleet favored right-sizing.
Container-host maintenance
The third effect is operational, and it shows up in how we keep the fleet patched. A multi-tenant host is hard to take down for maintenance precisely because it is full: draining it means relocating many tenants at once, several of which carry disruption budgets that limit how fast they can move, so a routine patch becomes a careful, coordinated evacuation. A single-tenant host runs exactly one task, with consolidation and defragmentation turned off, so draining it means relocating only the one workload, and we can automatically handle that when a new AMI ships. The remaining multi-tenant hosts are easier to maintain, too, because the workloads that were most sensitive to disruption are no longer stranded on them.
What it changes, and what it doesn’t
Single-tenant mode is a configuration, not a migration. A team moves a workload onto a dedicated node, and back, with a labeling change, without rewriting anything and without leaving Titus. That turns the isolation decision into a reversible setting, which is the opposite of the one-way door between Titus and EC2 that teams used to face. A team can try single tenancy for a quarter, measure it, and step back if the trade-off isn’t worth it for them.
What does not change is the contract. The Compute/Platform team still selects the instance type, patches the host, and sizes and scales the fleet underneath. The application team still uses the Titus API, the same delivery pipeline, and the same observability. Single tenancy is a new point on the isolation axis offered within the existing managed experience, not a separate product that the team has to learn and operate.
When a dedicated node is the wrong call
A dedicated node is a real cost, and single tenancy is not free isolation. Two things are worth weighing before reaching for it.
First, a single-tenant task does not get the whole machine; it gets the machine minus overhead. Every Titus container host, dedicated or shared, runs the platform sidecars, system services, the kubelet, and the host environment itself, and that overhead is a roughly fixed slice of CPU and a few gigabytes of memory. On a shared host, that slice is paid once and amortized across the many tasks running there. On a dedicated node, a single task handles it. Because the cost is fixed rather than proportional, it is punishing as a fraction of a small instance and negligible on a large one: a small dedicated node can lose tens of percent of its resources to overhead, while on the largest shapes it rounds to a couple of percent.
Second, because a task is placed on the smallest instance that fits it, there is usually a gap between what the task asked for and the next available shape, and on a dedicated node, that gap is pure waste, with no neighbors to soak it up. The two effects compound: fixed overhead plus the best-fit remainder set a ceiling on how much of a dedicated node a workload can actually use, and that ceiling is lowest exactly where people are tempted to reach for isolation casually, on small instances. However, this sizing waste can be reduced through coordination with the service owner as needed.
The guidance follows from the arithmetic. Single tenancy pays off for large, long-running, performance-sensitive, disruption-sensitive workloads, sized close to a node shape and run as fewer, larger replicas rather than many small ones. It is the wrong call for small, bursty, or highly elastic workloads, where the overhead fraction is high, the dedicated node sits mostly idle, and multi-tenant packing is both cheaper and faster to scale. This is also why the mode is allowlisted rather than a self-serve checkbox: the platform can keep workloads on the side of that line where they belong, and leave the ones that would gain little from a node of their own on the shared fleet, where they are cheaper to run.
Who’s using it
The first adopters are the workloads that motivated the work: real-time data infrastructure. Managed Apache Flink stream processing, streaming data connectors, and telemetry and logging pipelines were both the most frequent sources of network contention and the most damaged by it, because their recovery is expensive and their disruption budgets are tight. These are stateful, high-throughput jobs where a few seconds of starvation can cascade into minutes of catch-up, and where the platform’s own repacking used to be a source of disruption in its own right.
Moving them onto dedicated nodes removed the class of problem rather than mitigating it. The teams running them report stable operation, having previously seen intermittent, hard-to-attribute interference, and their jobs are no longer relocated by fleet repacking, removing a second, self-inflicted source of disruption. Latency-sensitive serving paths and a handful of GraphQL and edge services have followed for the same reason: a predictable tail matters more to them than a few points of bin-packing efficiency.
This is an ongoing rollout, not a finished one. We are widening the set of eligible workloads as we learn, using the largest production jobs as the stress test for the platform’s scaling assumptions, and watching the control-plane and EC2 launch-rate metrics as the count of small nodes grows. We have also been running periodic stress tests to exercise scaling ahead of real user workload, and making improvements to autoscaling and scheduling logic along the way.
What’s next
We are not done on either side of the tradeoff. On single tenancy, we are reducing launch latency with smarter pre-warming of common shapes, broadening the allowlist as scaling data holds up, and extending the model beyond long-running services as cost attribution and capacity stories mature. On the multi-tenant side, which remains the right default for most workloads, we are addressing the dimensions that hurt the most. The largest is the network: replacing HTB’s global-lock shaping with an eBPF-based Expected Departure Time approach that rate-limits by timestamping packets rather than contending on a lock, and pairing it with a lower-overhead container network device. We are also evaluating hardware cache and memory-bandwidth partitioning (Intel RDT and AMD PQoS) to give the kernel a real lever on the last-level cache, hardware GPU partitioning (NVIDIA MIG) for accelerator isolation, and continued work on the cgroup v2 IO controller for disk. This isolation benchmark lets us rank these by return on effort rather than by intuition, and show customers, in the numbers, that the shared fleet is getting quieter over time.
Single-tenant Titus is also a step toward something larger. Netflix’s Platform teams offer two ways to get compute: virtual machines on EC2 & containers on Titus. We want to replace that with a single Compute API that takes intent rather than mechanism into account: how much isolation a workload needs, how quickly it must launch, how long it can run without disruption, and what business domain it belongs to. The platform then makes placement and runtime choices, and can make globally optimal ones because it sees the whole picture.
Conclusion
Multi-tenancy is the right default for a container platform, and we will keep making it better for everyone. But the right default is not right for everything. Single-tenant Titus gives the workloads that need it the isolation of a dedicated VM, provisioned and patched by our existing node management, under the same API and the same managed experience, without taking away the freedom to change their mind. We can now point to the difference rather than describe it: a tail that stops moving under a noisy neighbor, a fleet that packs more densely once spreading is retired, and hosts that are faster and safer to patch. For the streaming and data systems at the heart of Netflix’s real-time platform, a room of one’s own turned out to be the feature that mattered.
Single-tenant Titus: VM-level isolation on a multi-tenant container platform was originally published in Netflix TechBlog on Medium, where people are continuing the conversation by highlighting and responding to this story.
What next for Australia after chastening defeat by South Africa?
Sexualised, violent threats: female Victorian MPs fear for their safety as they fight more than just next month’s election
Hostility from constituents is not new for the state’s politicians, including its premiers. But the alleged attack on Helen Haines has sent a chill down the collective spine
Get our new political email, free app or daily news podcast
On Monday night, Georgie Purcell shared a statement on social media in support of Helen Haines, who earlier that day had been allegedly attacked by a constituent in her regional Victorian electorate.
Purcell, a Victorian upper-house MP whose region partly overlaps with Haines’s federal electorate, wrote that the alleged attack had sent chills down her spine. Being a woman in politics, she said, had changed the way she moved through the world – where she parked her car, which route she took home, even whether she held public events at all.
Continue reading...The great moth revival: how bogongs have bounced back
This animated map shows the insect’s population exploding in Australia’s eastern states, with the endangered species coming back from the brink
If you live anywhere on the eastern side of Australia, you’ve probably noticed that bogong moths are back in a big way.
While we don’t yet have figures from ecologist-led surveys to compare with previous years, there is a wealth of data on the great moth revival being generated by citizen scientists across the eastern states.
Continue reading...Как я заставил ИИ-агентов собирать себе harness под конкретную задачу
Я дал Claude Code (Opus 5.5) тестовое задание: нарисовать в SVG сцену из «Бегущего по лезвию 2049». Агенты, которые я пробовал, провалили его одинаково: на настоящий кадр никто не посмотрел, рисовали по памяти и сообщали бездумно, что готово. Тогда я начал подсказывать агенту вопросы: есть ли документация, с чем сравнивать результат, когда остановиться. Из этих вопросов вырос AutoHarness — скилл, который заставляет агента подготовиться к задаче до того, как он начнёт её делать.
Читать далееI longed for my big break. Then a Nobel winner and my girlfriend showed me why success isn’t everything | Rebecca Shaw
I was reducing a creative life down to public recognition. Anne Carson’s career deserves more respect than that, and so does mine
I am one of those funny little people who is creative and has made the dubious decision to try to make a career out of it.
I didn’t fully commit until I was about 30, and I’ve spent the last 14 years in an up and down ride, trying to chip away until I reach the mysterious and elusive level of success where nothing bad happens ever.
Continue reading...Гари Ильес: robots.txt запрещает только краулинг, но не использование контента для обучения ИИ
Последние два года у владельцев сайтов сложилась коллективная привычка: дописать в robots.txt Disallow для GPTBot, CCBot и прочих AI-краулеров — и считать, что контент от ИИ закрыт. Гари Ильес из Google провёл границу, которая эту привычку обнуляет: robots.txt управляет краулингом, а не использованием контента для обучения (Search Engine Journal, 2026).
Should you use home equity to pay off credit card debt? Here's when it can backfire.
Black Bag by Luke Kennard audiobook review – brilliant Booker-shortlisted campus comedy
The author reveals his mastery of comic timing in his narration of this novel about a cash-strapped actor paid to live inside a black leather bag
The unnamed narrator of Luke Kennard’s novel is an out-of-work actor living in London. His last job was three months ago, he is behind with his rent and has “measured out my life in coffees I cannot technically afford”. So when he comes across an advert – “Male actor required for psychological enquiry. Non-speaking but discretion and devotion to restrictive performance requirements obligatory” – he offers his services.
The job, he discovers, is at a university working under a psychology professor named Dr Blend. There he must strip to his underpants and zip himself into a black leather bag, in which there are two eyeholes and further holes for his feet. The actor is expected to sit silently in the bag during seminars while students contemplate his presence.
Continue reading...Bruno Guimarães had sleepless nights before Newcastle exit but hopes for same ‘love’ at Arsenal
Midfielder says there were a lot of tears as he said goodbye at St James’ Park but he is enjoying the remorselessness at his new club
For Bruno Guimarães, it was a time to show his steeliness, to fix his eyes on the prize – even if he knew it would surely mean them welling up. And then some. It was a tumultuous summer for the Brazil midfielder. A fine World Cup on a personal level was marred by a crucial penalty miss in the last-16 loss against Norway. Now he had the dream move lined up to Arsenal but it could not happen without breaking some hearts at Newcastle.
Guimarães admits he lay awake at night as the emotions swirled. How could he leave Newcastle, the club where he made so many connections and enjoyed so many highs after joining from Lyon in January 2022? There were the Champions League qualifications and, above all, the Carabao Cup triumph in 2025 that ended a 70-year wait for a domestic trophy. On the other hand, how could he resist Arsenal and the prospect of competing regularly for the game’s top honours?
Continue reading...Zach Braff: ‘You can be talented and good-looking, but acting success is still like winning the lottery’
The Scrubs and Garden State star answers your questions about working with megastars, getting his hair to look good and being brutally killed on BoJack Horseman
How do you manage not to act starstruck when directing people like Morgan Freeman, Michael Caine and Harrison Ford? TopTramp
That’s where my acting comes in – I pretend that I don’t know how famous they are. Every actor really wants a leader. They want someone who knows the script really well, has a plan for how the scene is going to be executed, and – in the case of comedy – knows how to make it funny. The last thing any of those guys wants is someone coming in starstruck and wide-eyed. So I use my acting skills to pretend I’m not starstruck and treat them like normal people.
Your Fake Doctors, Real Friends podcast was a real help through lockdown. You were very emotionally open and personal; it was like catching up with friends. I still think about your line that making it in acting, even if you’re talented and good-looking, is like winning the lottery. Do you think that early 00s Zach Braff would make it in the present day the way you did? KamesJ
Back then, the broadcast networks were making so many pilots, at least it was work for people. Now, I think it’s a much harder landscape to break through. I firmly believe that you can be talented and good-looking, but success is still like winning the lottery. I know plenty of brilliant actors whose lottery ticket hasn’t come up yet. I started auditioning at 14 and barely got anything for years, so I’ve always felt very lucky.
[Перевод] Фонд OpenAI вложился в нейроимплант против рака мозга
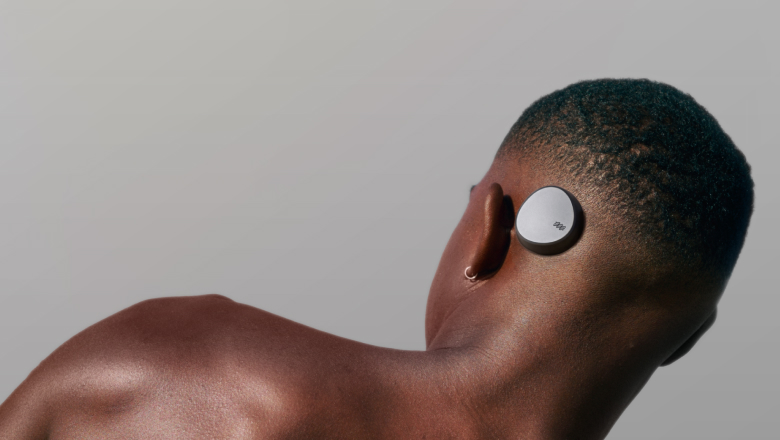
Нейроинтерфейсы обычно обсуждают как способ вернуть человеку возможность управлять компьютером или общаться после потери речи. Coherence Neuro разрабатывает устройство с другой задачей: отслеживать опухоль по электрической активности тканей и воздействовать на неё стимуляцией. Стартап привлёк 45 млн долларов, чтобы продвинуть технологию к длительным исследованиям на людях.
Читать далееWATCH: Trump rallies in Iowa with GOP Senate candidate Ashley Hinson
Developer platform Railway urges ‘all users’ to revoke secret keys after cyberattack
The Cornell 7 and the Problem with Writing as Punishment
Justice is elusive, and there are few clearer examples of this than when people who commit acts of sexual violence are given rote tasks as a means of atonement.
Recently, the “Cornell 7” case has inspired new conversations about what accountability and atonement involve. When college administrators investigated a report of sexual violence, some of the alleged perpetrators were reportedly assigned to write “reflection papers,” along with other punishments. The writing assignments drew such ire that Cornell issued a statement stating that "none of the individuals charged were offered the opportunity to write essays as a sole consequence of their involvement."
I am a survivor of childhood sexual abuse, which started when I was 11 years old. Abuse from my step-father went hand-in-hand with punishment. He knew how much I loved words, reading, and writing, and began to use them to discipline me.
Our household was governed by an elaborate set of rules. We were not allowed to speak during dinner without permission. We were required to stand while playing board games. Our bedrooms were inspected every evening, and our beds had to be made with hospital corners.
Any infraction could result in punishment. One of the preferred methods was to require me to write an essay outlining what I had done wrong and how to correct my misdeeds. If I didn't wash the dishes carefully enough, I would have to write an essay about why I needed to take better care when cleaning up after dinner.
Other times, I was ordered to write the same sentence hundreds of times.
If I complained about dinner, I had to write 100 times, “I will appreciate my mother’s cooking.”
If I made fun of one of my siblings, I had to write 250 times, “I will not make fun of my brother.”
And if I resisted attempts to assault me, the punishment could be a thousand repetitions of “I will listen.”
I was being punished for trying to protect myself from the person who was abusing me. In doing so, I learned that writing the correct words was not the same as believing them. I could produce an essay explaining what I might have done wrong and promise to be better, but it didn’t mean that I believed that I misbehaved. It meant that I understood what was required of me. The punishment was complete when the writing was complete, but whether I had learned anything was beside the point.
More than 50 years later, I find myself wondering what we believe an essay can accomplish when it is assigned in response to allegations of sexual violence. Cornell’s disciplinary proceedings have resulted in different sanctions for different students, including expulsions and suspensions. “Reflection papers” were among the educational requirements imposed on some students.
But what, exactly, can an assigned essay demonstrate?
An essay can be thoughtful and persuasive; it can express regret, recognize harm, and promise change. But how do we know whether the person who wrote it believes any of what is written? What happens when completing an assignment becomes a substitute for demonstrating genuine understanding or changed behavior?
I have spent my adult life writing, teaching, and interviewing people about their lives. I believe in the ability of language to help us understand ourselves and one another, and I know how easily language can be used to conceal the truth.
My abuser understood the power of words, and used them to dictate the terms of my obedience. He controlled what I was allowed to say. He warned me that no one would believe me and threatened violence against those I love if I spoke out. I believed him, and I remained silent and ashamed.
I was required to write about my smallest infractions while being forbidden, through fear, to speak about the most terrible thing happening in my life. And the person who demanded that I explain my wrongdoing was the person committing the most serious wrongdoing of all.
This is why the relationship between language and power matters so much to me. The person with authority often gets to decide what constitutes an acceptable explanation, a credible account, or a sufficient expression of remorse.
Jane Doe, the young woman at the center of the Cornell case, reported the incident to university police in 2024. Since then, the timing and content of her disclosures have become subjects of intense public scrutiny. Public debate has focused in part on differences between her initial statements and her subsequent allegations.
I cannot speak for her, and our experiences are different. But I understand how fear can determine what someone is willing to reveal, even when she desperately needs help.
There is something troubling about how much we expect words to prove in cases of sexual violence. We scrutinize the accounts of those who report abuse, searching for inconsistencies. Now we are asking those found responsible for misconduct to demonstrate understanding through written reflection.
I believe writing can lead to meaningful change. But an essay is evidence that someone has completed an assignment. It cannot establish whether that person understands the harm they have caused or whether their behavior will change.
Why are we putting so much faith in the words people are required to write, while questioning the words that others struggle to say?
Чёлка MacBook как пульт для ИИ‑агентов: Claude Code, Codex, Cursor и Copilot в одном месте
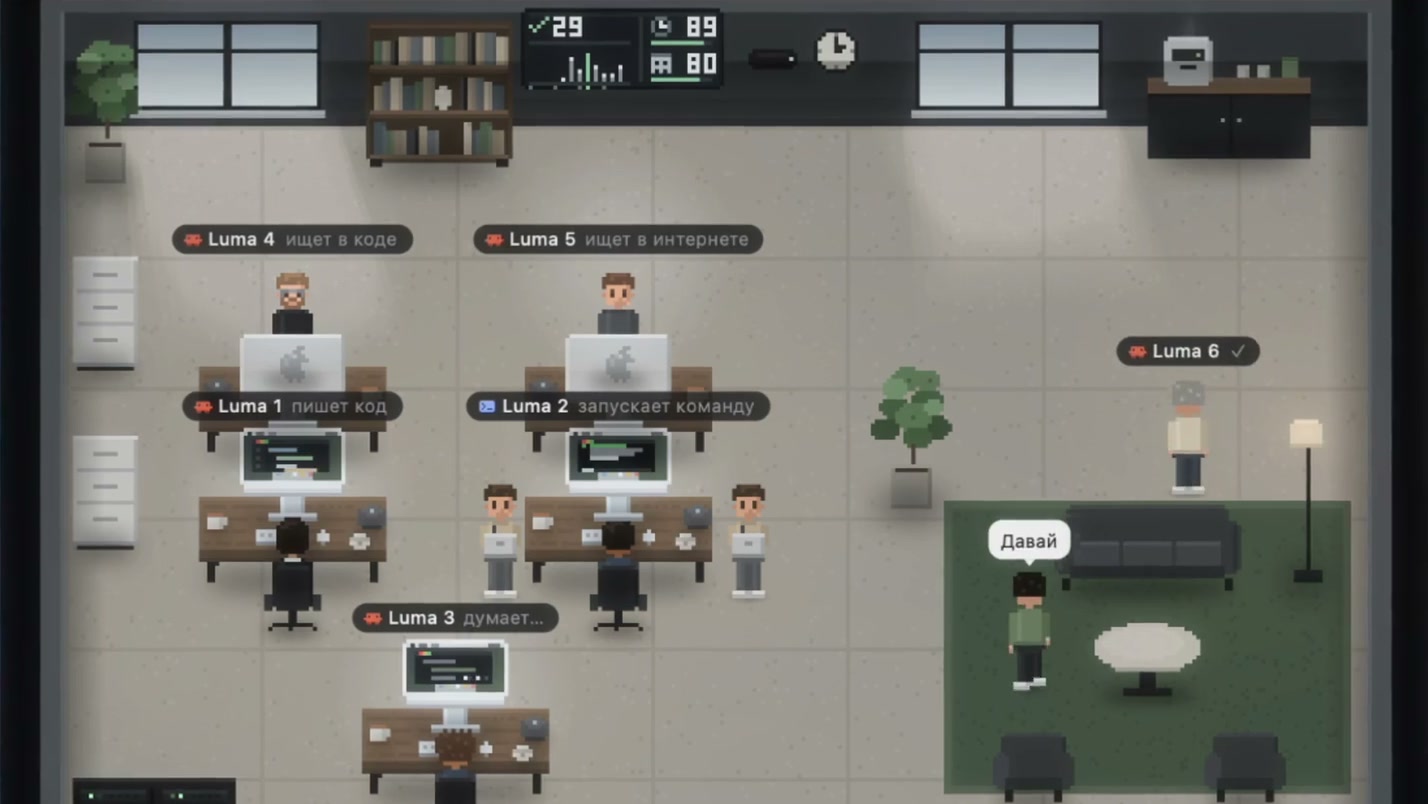
Вы запускаете трёх агентов сразу. Один закончил. Второй уже десять минут ждёт вашего «да». Третий упал, и вы об этом не знаете. Узнаёте, только когда по очереди переключаете окна.
Мы сделали Lumio, чтобы больше так не работать. Это бесплатное приложение для Mac, которое превращает чёлку MacBook в пульт для ИИ-агентов. В версии 1.2 к Claude Code и Codex добавились Cursor и GitHub Copilot в VS Code. Теперь все четыре видны в одном месте, и почти на всё можно ответить, не открывая редактор.
Читать далееBody camera footage shows moments leading up to 1-year-old's death in police shooting
In final Michigan Senate debate, El-Sayed and Rogers question each other's loyalties
Opinion | Republicans, Act on Russia
Opinion | Obama Has Always Been Careful With Words
High-ranking Virginia Democrat charged in public corruption case
Ilhan Omar says she plans to move out of Washington home after federal raid
Democratic lawmaker says family’s safety is at risk amid death threats and raid making apartment’s address public
Minnesota congresswoman Ilhan Omar said she plans to move out of her Washington DC apartment after federal agents raided her residence last week as part of a larger immigration investigation.
“I mean obviously, I can’t continue to live there,” Omar told MS Now in an interview that aired on Wednesday. “So we have to figure out where to move to, because our address has been public and with the death threats that I deal with, it’s no longer going to be feasible to be in that house and have my kids, like, visiting off and on, having people track them.”
Continue reading...Tougher punishments for criminals who refuse to attend sentencing backed by victim's family
Ilhan Omar says 'bizarre' pre-dawn raid on her home is forcing her to move out
Ossoff pulls ahead of Collins in new Georgia Senate poll
Hazardous fumes still leaking from Toledo chemical tank
Feds charge powerful Virginia Democrat in alleged drug scheme
Champions League review: PSG take a hit, Man City’s empty seats and teenage hope for Liverpool
The reigning champions must deal with the absence of Khvicha Kvaratskhelia for some time, while fans at Anfield were thrilled by Rio Ngumoha
Paris Saint-Germain beat Barcelona 4-2 on Tuesday, but the reigning champions lost the best player in last season’s tournament, Khvicha Kvaratskhelia. This autumn has seen much lobbying for the Ballon d’Or, with the Georgian a popular choice, despite his absence from the World Cup. He is expected to be out for six months, although Rodri’s comeback from serious injury – he was rested by Barcelona on Tuesday until coming off the bench in the 60th minute – shows it can take far longer than that for players to rediscover their highest level.
Continue reading...Ilhan Omar says 'bizarre' pre-dawn raid on her home is forcing her to move out
Claude Duet app is Anthropic’s bet on agents
Greetings from the Brazil-Argentina border, where waterfalls are flowing at near-record rates
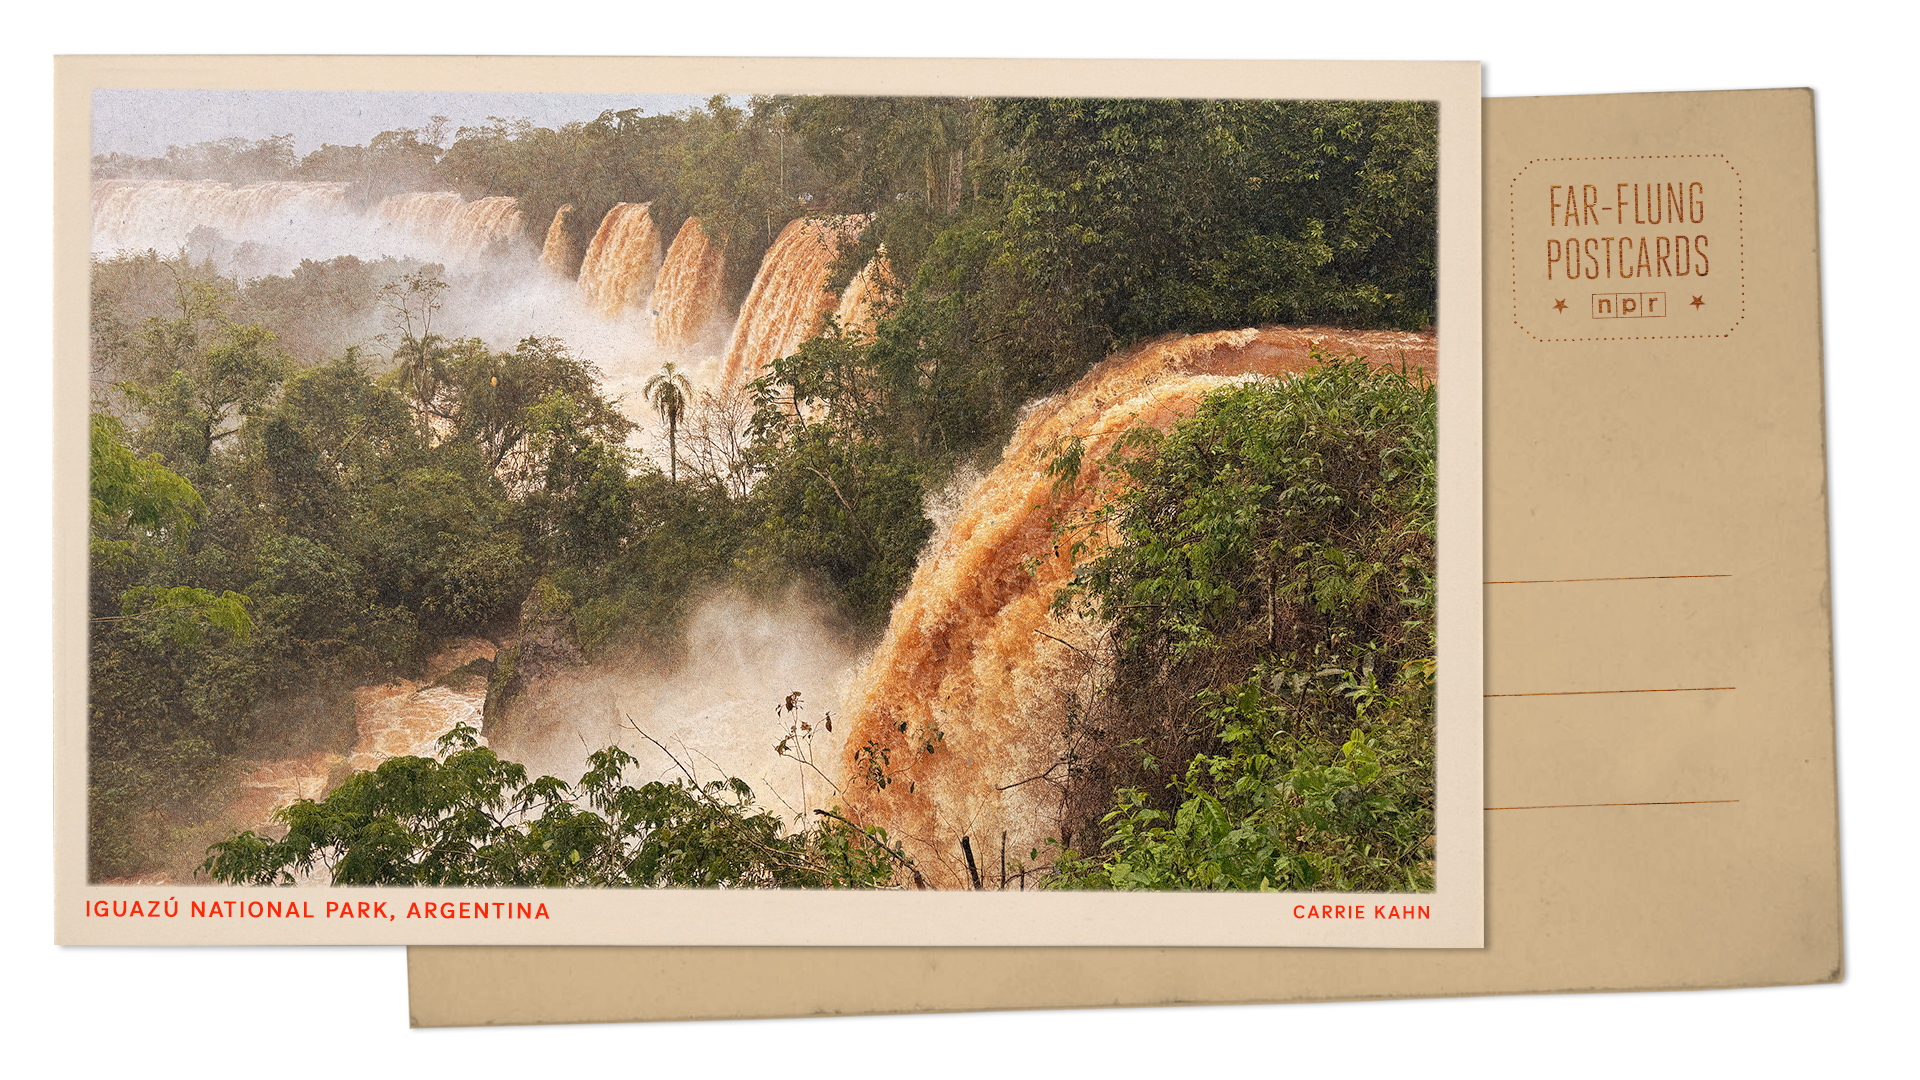
The Iguazú Falls span more than a mile across both countries. A rain-soaked October, which scientists link to the Super El Niño, has sent near-record volumes of water surging over the towering cliffs.
